Nairobi, Kenya · Open to global opportunities

I build secure platforms that help teams ship, observe and recover with confidence.

Senior DevOps, DevSecOps and Platform Engineer with 7+ years of experience designing, securing and operating cloud-native platforms across AWS, Azure and Kubernetes.

Kubernetes✦GitOps✦DevSecOps✦Observability✦SRE✦Recovery engineering

From fragile delivery to dependable platforms

Engineering the path from commit to production—and back again when recovery matters.

I design and operate the infrastructure, automation and guardrails behind reliable software delivery. My work spans Kubernetes, CI/CD, GitOps, infrastructure as code, software supply-chain security, observability and cloud operations.

I focus on systems teams can operate: immutable releases, auditable promotion, useful telemetry, practical security gates, documented runbooks and recovery workflows that are tested rather than assumed.
70+ repositoriesStandardised enterprise build, test, security, artifact and deployment workflows.
Highly available RKE2Built bare-metal clusters with Kube-VIP, MetalLB, Longhorn, Ceph and MinIO.
Secure deliveryEmbedded source, dependency, container, infrastructure and runtime controls into CI/CD.

Capability groups

A platform engineering toolkit organised around outcomes.

01

Cloud & platform engineering

Cloud-native foundations, orchestration, traffic management and autoscaling.

AWS · Azure · GCP · OCI · Kubernetes · AKS · EKS · RKE2 · OpenShift · Helm · Kustomize · Istio · KEDA · HPA

02

Delivery, GitOps & automation

Reviewable infrastructure and controlled, repeatable releases with Git-based rollback.

Jenkins · Azure DevOps · GitHub Actions · GitLab CI/CD · ArgoCD · FluxCD · Terraform · Ansible · PowerShell · Bash · Python

03

DevSecOps & identity

Controls spanning source, dependencies, images, infrastructure, identity and runtime.

SonarQube · CodeQL · Gitleaks · Trivy · Checkov · OWASP ZAP · Falco · Vault · Keycloak · RBAC · CycloneDX SBOM

04

Observability & SRE

Metrics, logs, traces, service objectives and burn-rate signals for incident response.

OpenTelemetry · Prometheus · Grafana · Loki · Tempo · ELK · Alertmanager · SLOs · Burn-rate alerting

05

Data, storage & recovery

Stateful services, encrypted backups and restore validation designed for recoverability.

PostgreSQL · SQL Server · Redis · MinIO · Ceph · Longhorn · S3-compatible storage · Velero

Verified career history

Delivery, security and reliability across cloud and Kubernetes environments.

  1. Nov 2025 — Present

    Senior DevOps & DevSecOps Engineer

    Avantech Ltd · Remote

    Designing enterprise CI/CD across 70+ repositories; operating AKS with Helm and ArgoCD; integrating DevSecOps controls, observability, SLOs and automated Windows application testing.

  2. Jan 2025 — Oct 2025

    Senior DevOps Engineer

    Crafted Systems Ltd · Nairobi

    Built highly available bare-metal RKE2 clusters and operated GitOps, secrets, distributed observability, autoscaling, storage and data services.

  3. Jul 2023 — Dec 2024

    Senior DevSecOps Engineer

    Nathan Digital · Nairobi

    Automated AWS infrastructure, applied Kubernetes and cloud security controls, embedded CI/CD security gates and supported ECS/EKS migration.

  4. Apr 2022 — Jun 2023

    DevOps Engineer

    Uamuzi Foundation · Nairobi

    Automated Azure infrastructure, implemented ArgoCD GitOps and improved container orchestration, testing and production monitoring.

  5. Apr 2019 — Mar 2022

    DevOps Engineer

    ISON Technologies · Nairobi

    Built Jenkins delivery pipelines and automated Kubernetes delivery across AWS and Azure while strengthening TLS, secrets and observability.

Portfolio case study · LitanovoWorking platform · Active development

OBSERVEX

Engineering ownership

Operational and security context in one platform.

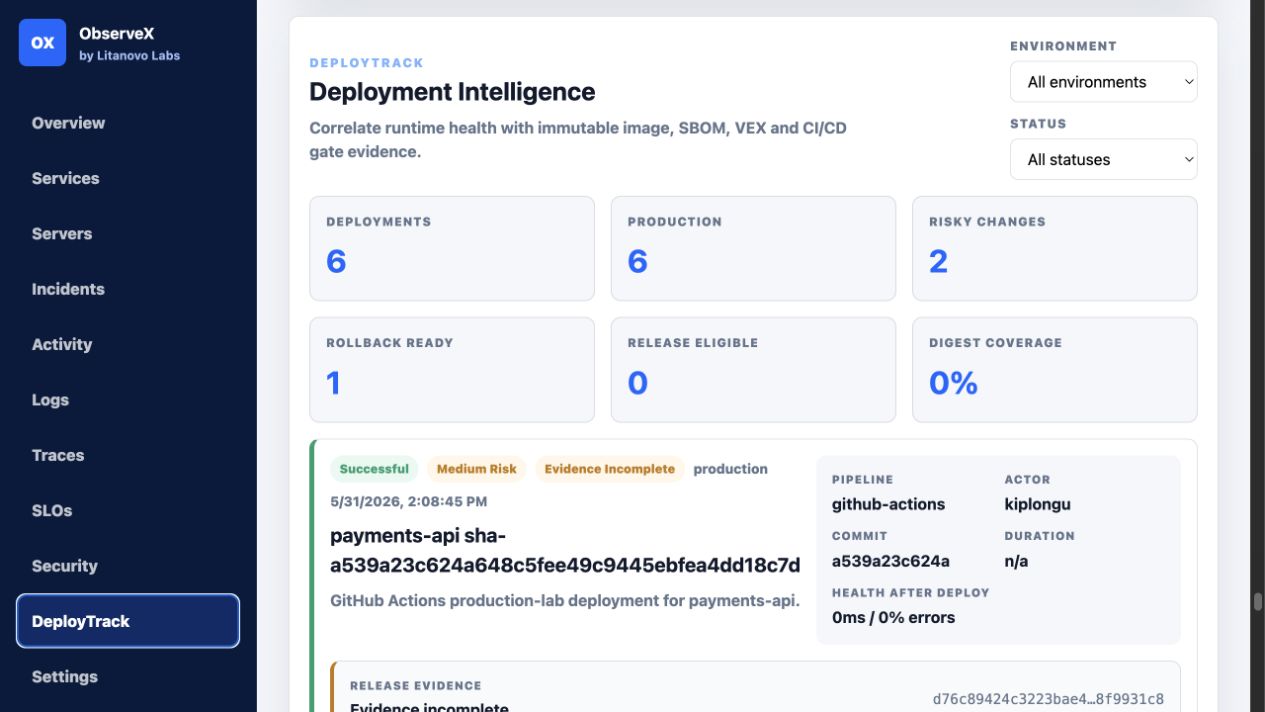
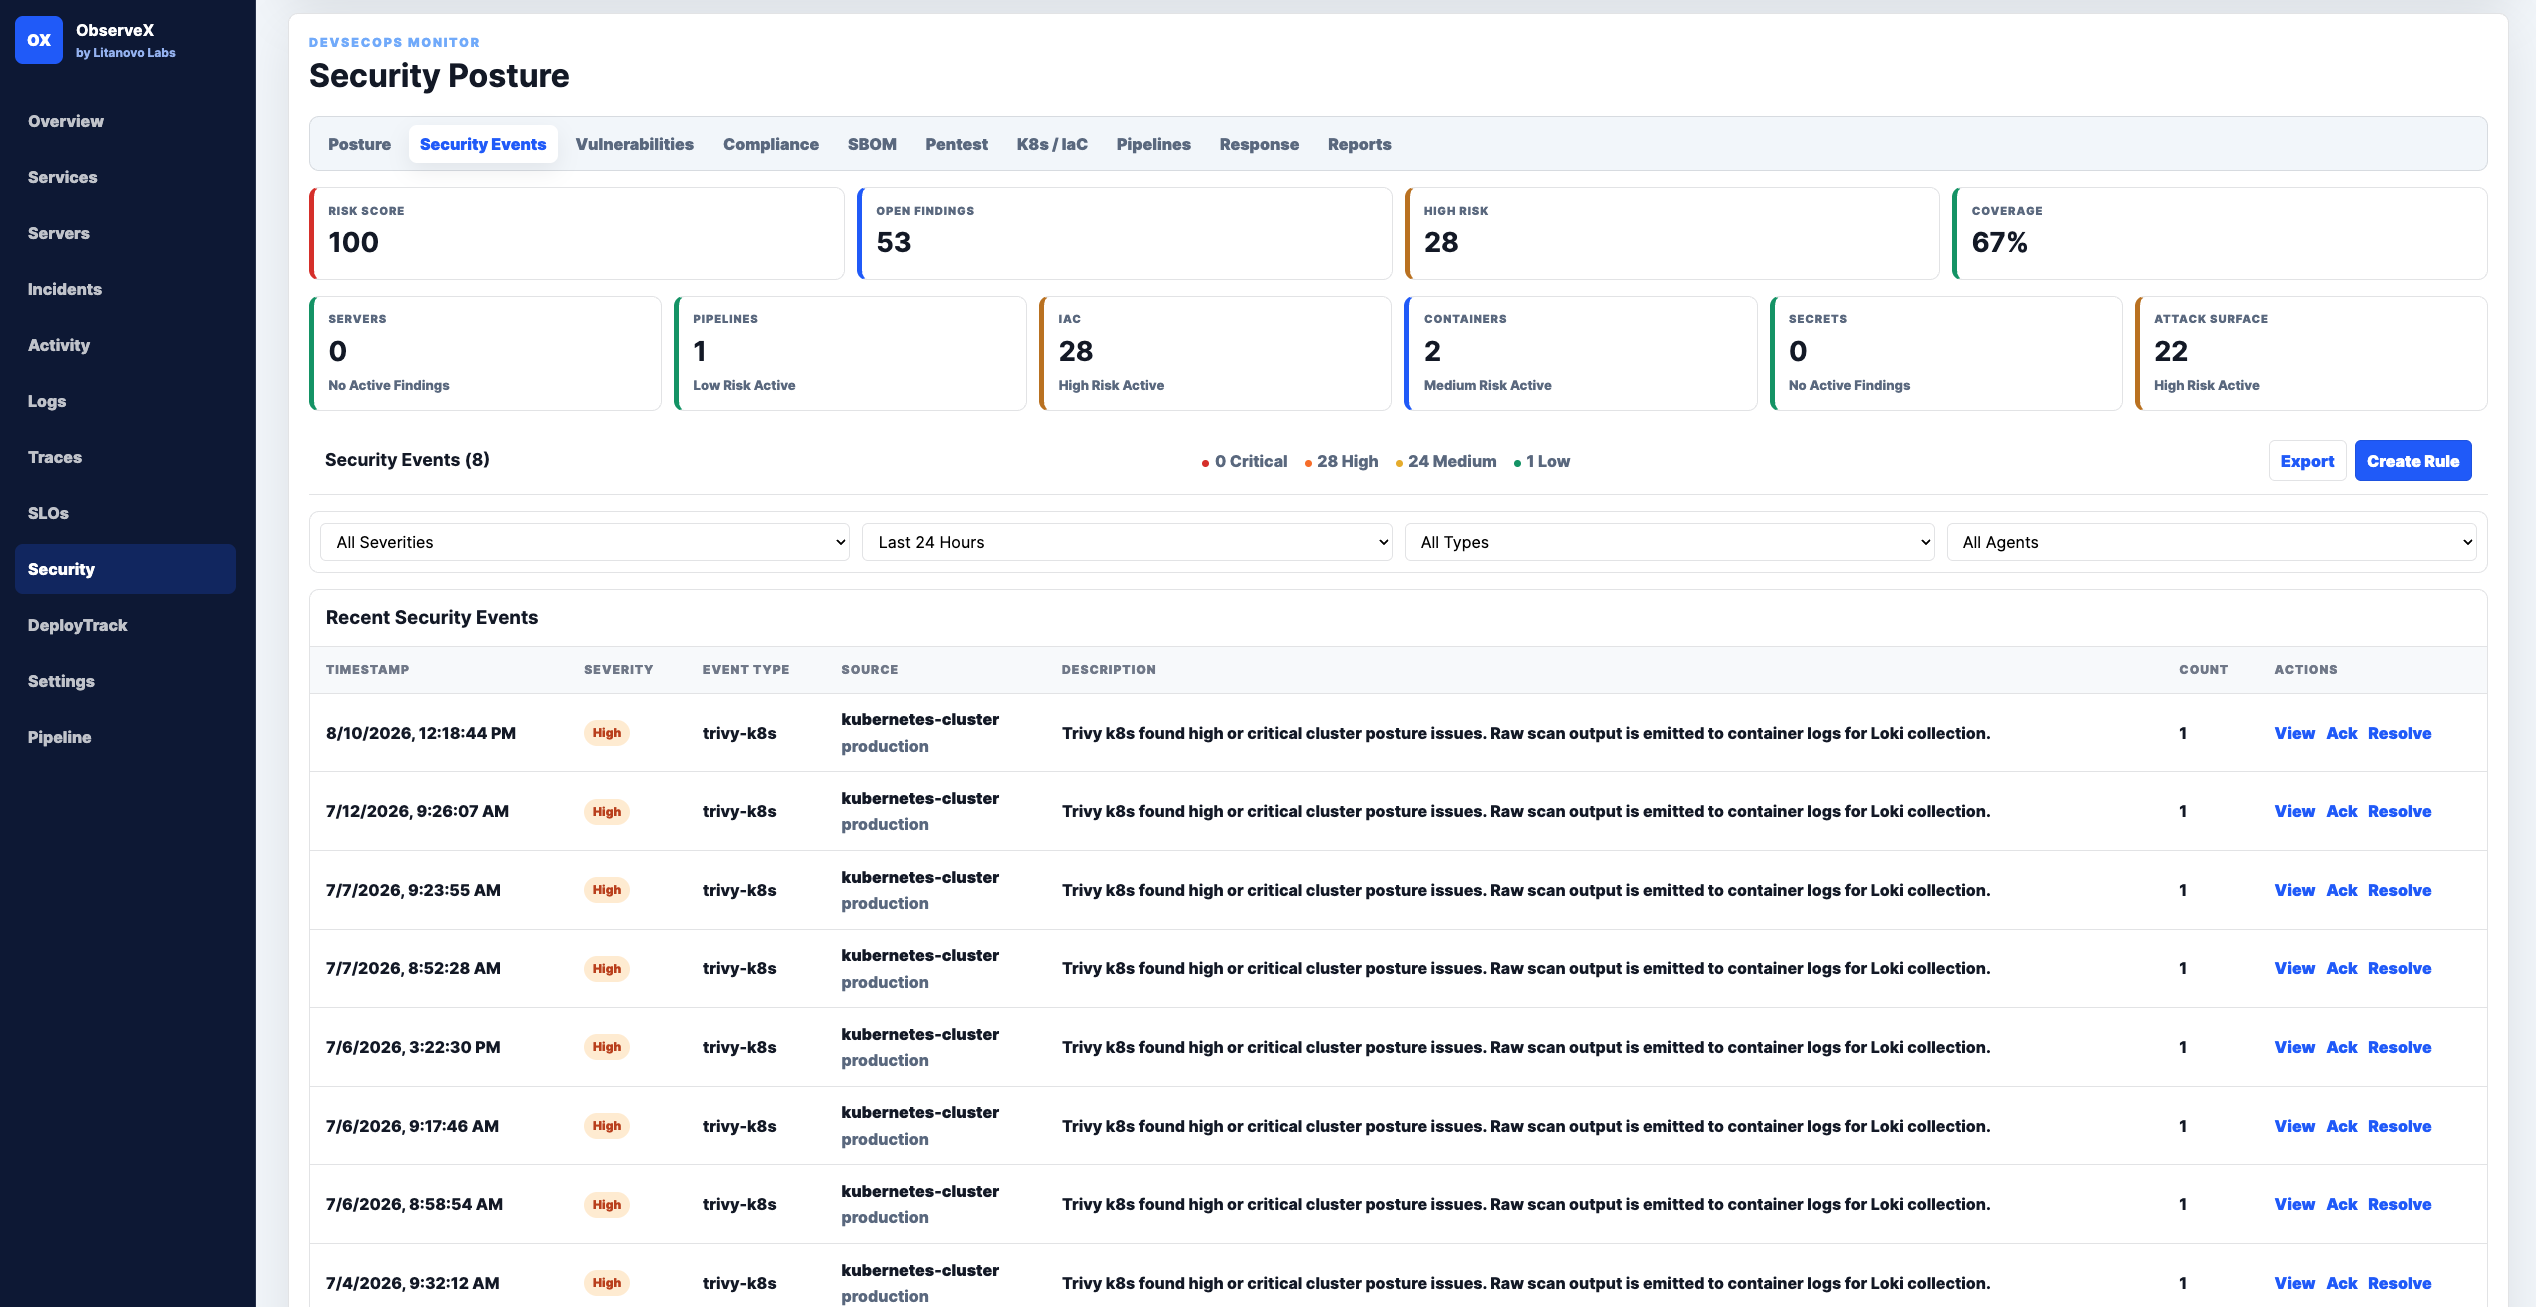
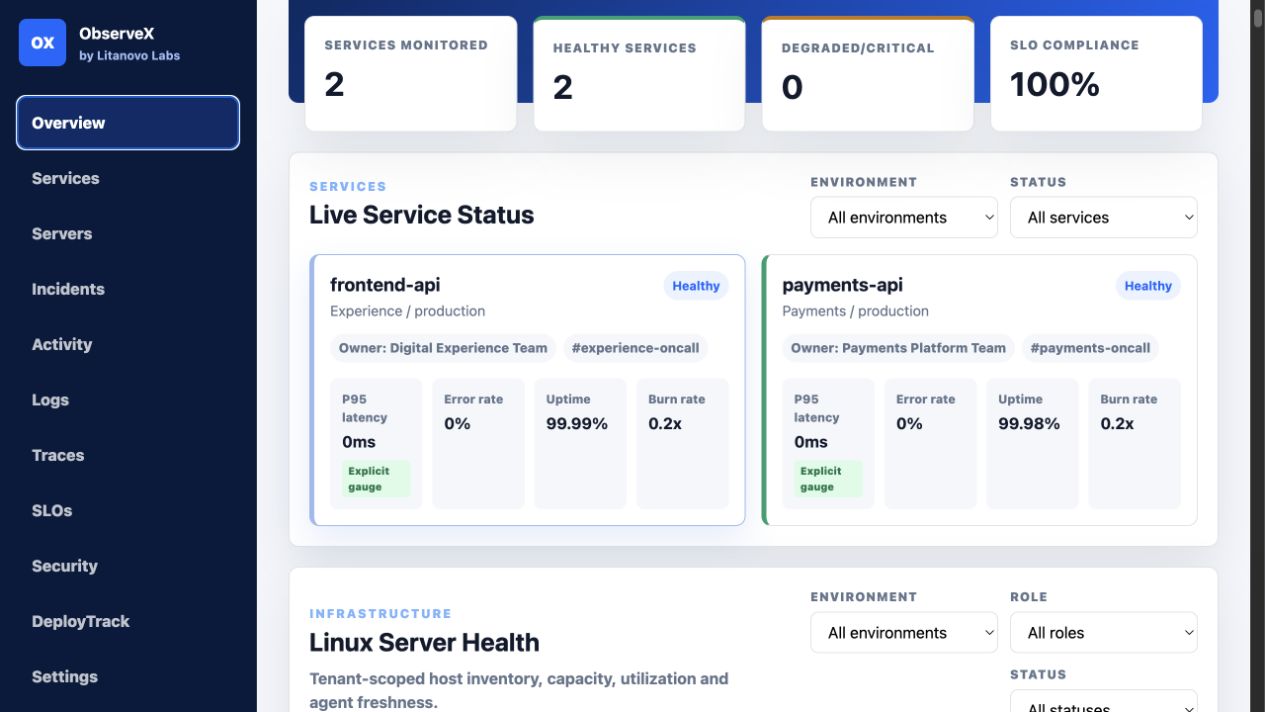
ObserveX is an observability and DevSecOps platform I am building under Litanovo. I own architecture and implementation across application workspaces, APIs, identity, delivery, telemetry, security evidence and recovery workflows.

The problem

Engineering signals are fragmented across tools and teams.

Service health, incidents, logs, traces, SLOs, security findings and deployment evidence often live in separate systems. That slows triage and weakens release context.

ObserveX creates a tenant-aware operational workspace that connects those signals without duplicating every specialist tool.

System architectureIdentity-aware workspaces connected to telemetry, delivery and recovery systems.
StatePostgreSQLTenant isolation
TelemetryOpenTelemetryPrometheus · Loki · Tempo · Grafana
DeliveryArgoCD + HelmKubernetes · Istio · immutable images
RecoveryMinIO + VeleroBackups · restore verification
01

Application & tenancy

React workspaces separate concerns while Node.js APIs provide shared contracts. PostgreSQL tenant isolation and Keycloak identity context scope organisation data.

02

Delivery & rollback

Helm packages Kubernetes workloads. ArgoCD automates staging while production promotion remains controlled. Immutable images and Git history provide auditable rollback.

03

Telemetry & mesh

OpenTelemetry connects application signals to Prometheus, Loki and Tempo. Grafana supports deeper analysis and Istio provides the service-mesh layer.

04

Security evidence

CodeQL, Gitleaks, Trivy, Checkov and OWASP ZAP gate different layers. CycloneDX SBOMs connect releases with security evidence.

05

State & recovery

PostgreSQL backups are incomplete until restore verification succeeds. MinIO stores recovery artifacts and Velero supports cluster recovery workflows.

06

Operational model

Services, servers, incidents, logs, traces, SLOs, security and deployment tracking are connected workflows—not isolated dashboards.

What I learned

Integration boundaries matter more than dashboard count.

Identity, tenant scope and evidence must survive every handoff between delivery, security and operations.

Trade-offs

Progressive integration over premature consolidation.

Specialist systems remain sources of truth. Controlled production promotion favours auditability over maximum speed.

Remaining work

Hardening continues.

Priorities include load and failure testing, recovery drills, policy enforcement, evidence retention and broader tenancy testing.

Certifications and training

Technical foundations reinforced through continuous learning.

  • CKACertified Kubernetes Administrator
  • KCNAKubernetes and Cloud Native Associate
  • PCAPrometheus Certified Associate
  • AWSCertified SysOps Administrator
  • OCIDevOps Professional
  • OCICyberOps Associate

Additional training

Linux Foundation Implementing DevSecOps (LFS262) · Introduction to DevSecOps (LFS144) · Introduction to DevSecOps for Managers (LFS180) · Linux Server Management and Security

EducationBSc, Information Communication Technology — Jaramogi Oginga Odinga University of Science and Technology · Second Class Upper Division

Let’s build something dependable

Have a platform challenge worth solving?

rodgersbiwott2016@gmail.com